Enterprise Trust & Compliance with Boudica AI
In the race to innovate, the biggest risk isn't being slow: it’s being compromised.
Under the EU AI Act, non-compliance can trigger penalties reaching up to €35 million or 7% of global annual turnover. Yet, mainstream AI relies heavily on middleware wrappers, keyword filtering, and "Private Cloud" hosting to claim regulatory readiness.
For Regulated Industries & any business working with confidential IP, this is unacceptable.
Compliance-Grade AI for Regulated Enterprises
Boudica replaces cloud-hosted liabilities with a compliance-by-design engine to deliver total data path isolation, deterministic auditability, & permanent model ownership inside your firewall or within your own private cloud instance.
Own Your Own Intelligence.
Key Value Propositions
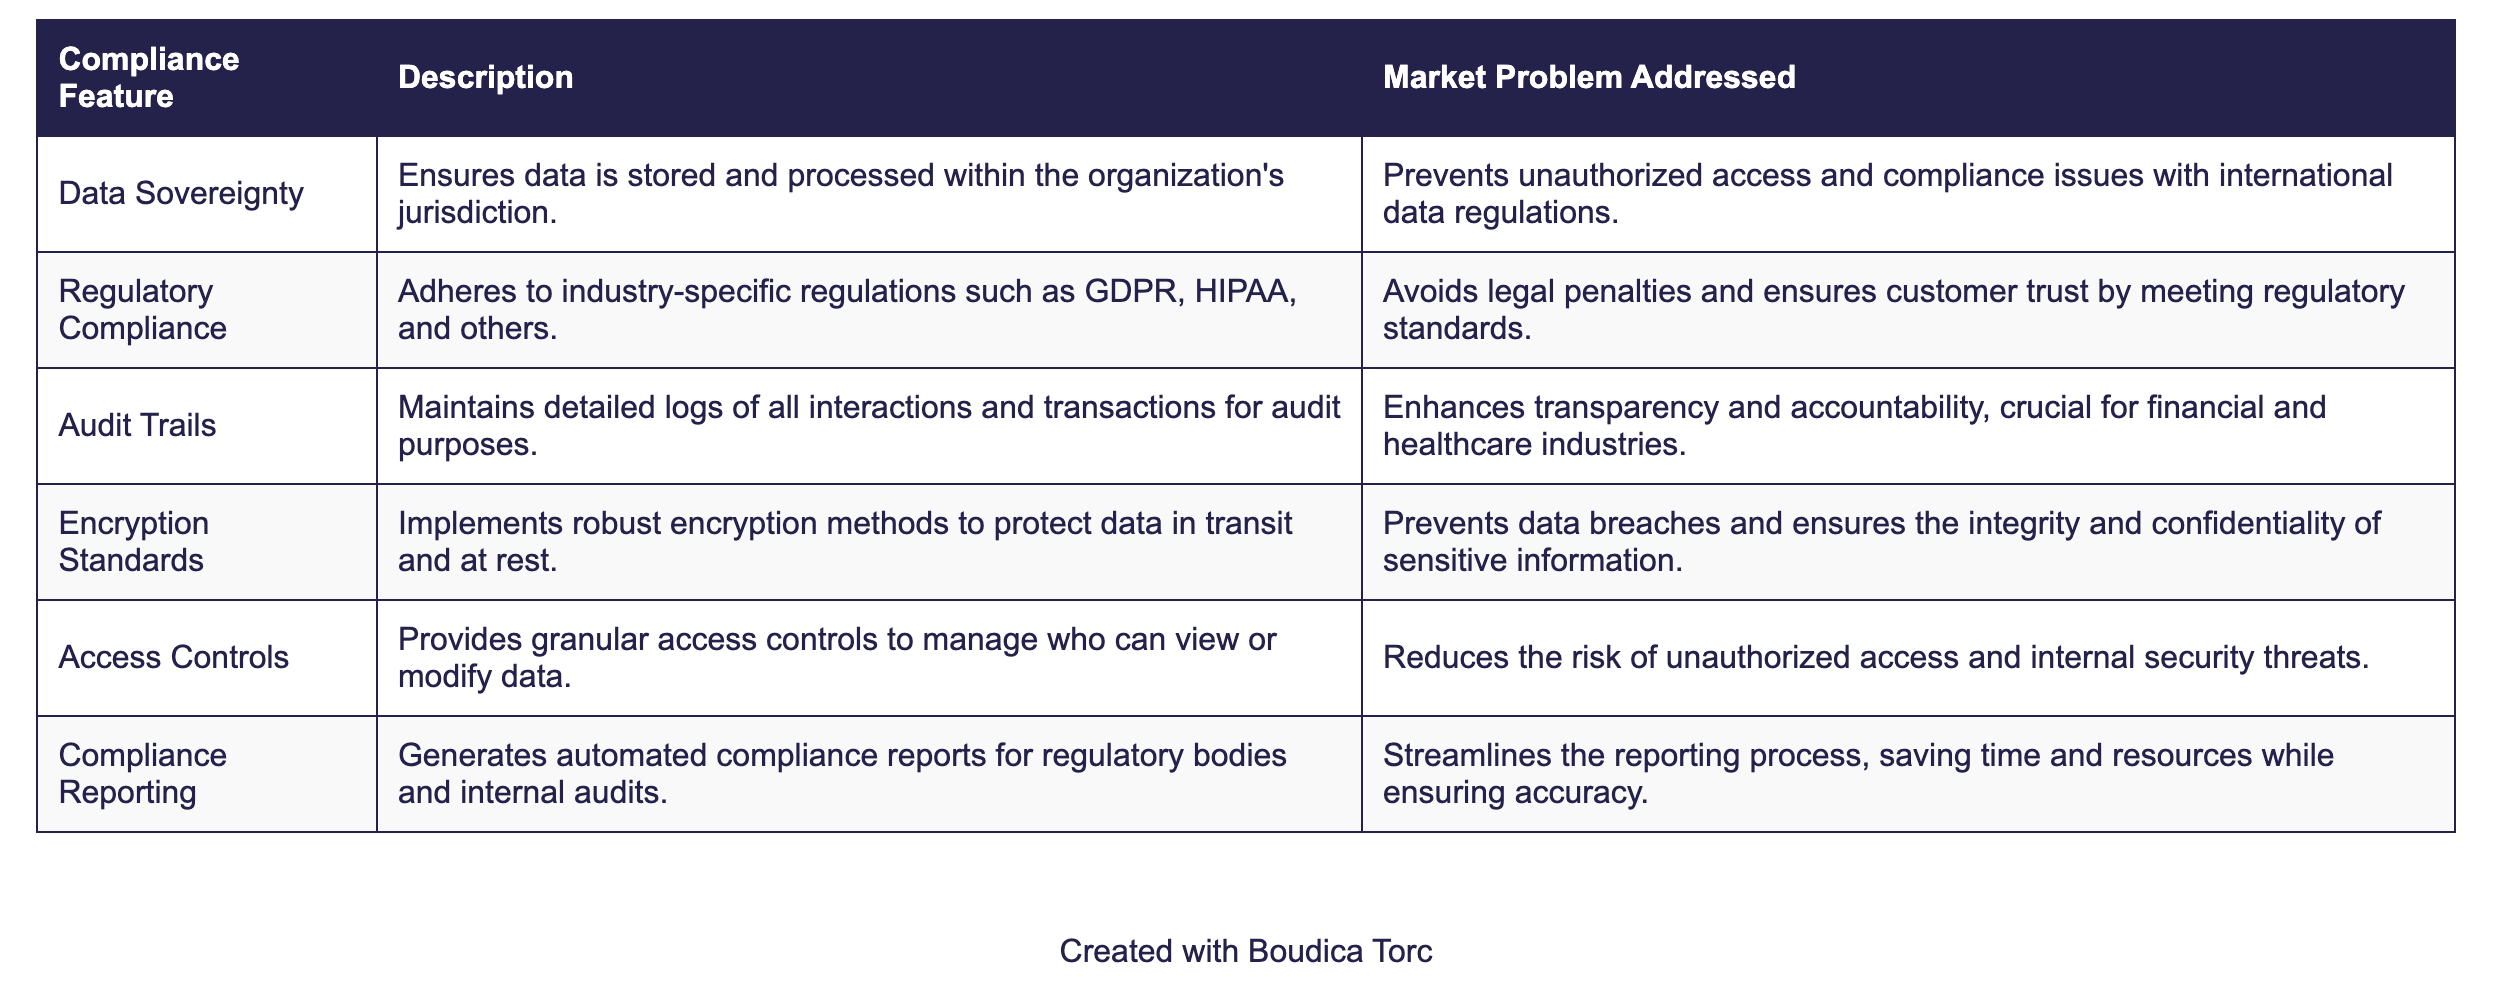
Radical Data Transparency
Boudica's models are built on copyright-cleared and verifiable foundations. Every data source is indexed with explicit licenses of use, providing the provenance required by regulatory bodies.
On-Premise Perimeter Execution
Operating fully on-premises with zero external API calls, Boudica ensures raw prompts, embeddings, and context never escape the corporate control. This eliminates third-party telemetry leakage and protects proprietary intellectual property from exposure.
Deterministic RAG Verification Loop
Through Factuality Grounding, outputs are cited back to authenticated internal company documents. Retrieval tracking also logs the precise source files used for every answer, giving risk officers a click-to-verify defense against hallucinations & an audit trail across the reasoning path.
Localized AI Observability & Forensic Logging
Full-text capture of prompts, context sources, & model versions strictly on your local infrastructure to provide an immutable audit trail for internal forensic analysis without external exposure of operational records.
Fine-Grained Role-Based Access Control (RBAC) & Governance
Zero-Trust Document Access & Departmental Scoping
Knowledge Base indexing does not imply universal visibility. Boudica operates on a strict deny-by-default access model, ensuring unclassified documents remain completely hidden.
Domain administrators can define granular access permissions down to the role, department, or individual user, complete with automatic expiry dates and immediate grant revocation.
Multi-Tenant Scoped Administration
Multi-organisation and cross-department deployments maintain total data isolation. Enforced directly at the database level rather than hidden in the UI, administrator views, analytics, and RAG corpuses are rigidly scoped to each specific domain.
Active Model Guardrails & Real-Time Content Safety
Automated Content-Safety & Risk Observability
Data isolation is paired with active runtime protection. Boudica continuously scans prompts against built-in content-safety layers. Any flagged activity or policy breach is immediately escalated to the administrator portal under 'Security Risk Alerts' with detailed risk rationales, providing full operational oversight over model usage and prompt safety.
Real-Time Answer Verification
Verbatim Mode & Factuality Precision
Eliminate plausible guessing in high-risk contexts. Users can enforce Verbatim Mode, instructing the inference engine to answer using only text explicitly verified within retrieved internal documents. If exact source evidence does not exist, the system safely declines to answer rather than paraphrasing or extrapolating.
Corpus Auditability & Deletion Management
Live RAG Corpus Auditing & Instant Deletion
Maintain complete control over retrieved knowledge assets. Through the RAG Corpus Management interface, risk officers and data stewards can inspect every searchable chunk, source document, and topic currently indexed by the model. Any outdated or sensitive entry can be deleted instantly, removing it from the retrieval pipeline in real time.
Secure External Data & Connector Isolation
Sandboxed Third-Party Connectors
Extend intelligence to outside platforms without compromising security. External data connectors operate inside disposable, network-isolated containers subject to strict administrator approval. No third-party connector can bypass Boudica's built-in extraction, content-safety, and RBAC governance pipelines.
Use Cases
High-Risk Financial Services & Credit Scoring
By deploying Boudica AI on-premises with deterministic RAG citations and localized model versioning, regional banks automate loan risk evaluations while fully satisfying high-risk AI mandates under the EU AI Act. This replaces slow, manual compliance reviews with instant, legally defensible audits while completely eliminating the risk of multi-million euro regulatory penalties.
Pharmaceutical Research & Intellectual Property Protection
Operating entirely within an enterprise's air-gapped GPU infrastructure, Boudica executes Native LoRA fine-tuning on proprietary patent filings and clinical notes without sending data to a third-party black-box. This eliminates competitive IP leakage risks while building a compounding, permanent corporate knowledge asset on predictable costs.
Cross-Border Healthcare & GDPR-Compliant Patient Intelligence
Equipped with forensic prompt logging and isolated context pools, localized models allow medical teams to analyze complex clinical records without triggering cross-border data transfer violations. Healthcare networks achieve 100% GDPR data sovereignty compliance while reducing documentation overhead and eliminating variable cloud token charges.
Technical Explainer: PGBC Immutable Audit Logs
OmniIndex Developed our own Web3 Database for Enterprise-Grade Data Management & Immutable AI Auditing
Cryptographically Linked Immutability
- Data is stored as immutable blocks in a decentralized chain.
- Each block is cryptographically linked to the previous one, preventing tampering or ransomware attacks.
Multi-Node Resilient Decentralization
- Data is replicated across multiple nodes, eliminating single points of failure.
- In case of node compromise or failure, data is instantly recovered from other peers, ensuring zero data loss and continuous availability.
All rights reserved © 2026 OmniIndex