Boudica AI Data Sovereignty & Security
Sovereign AI Perimeter: Absolute Data Isolation & Compliance-Grade Governance
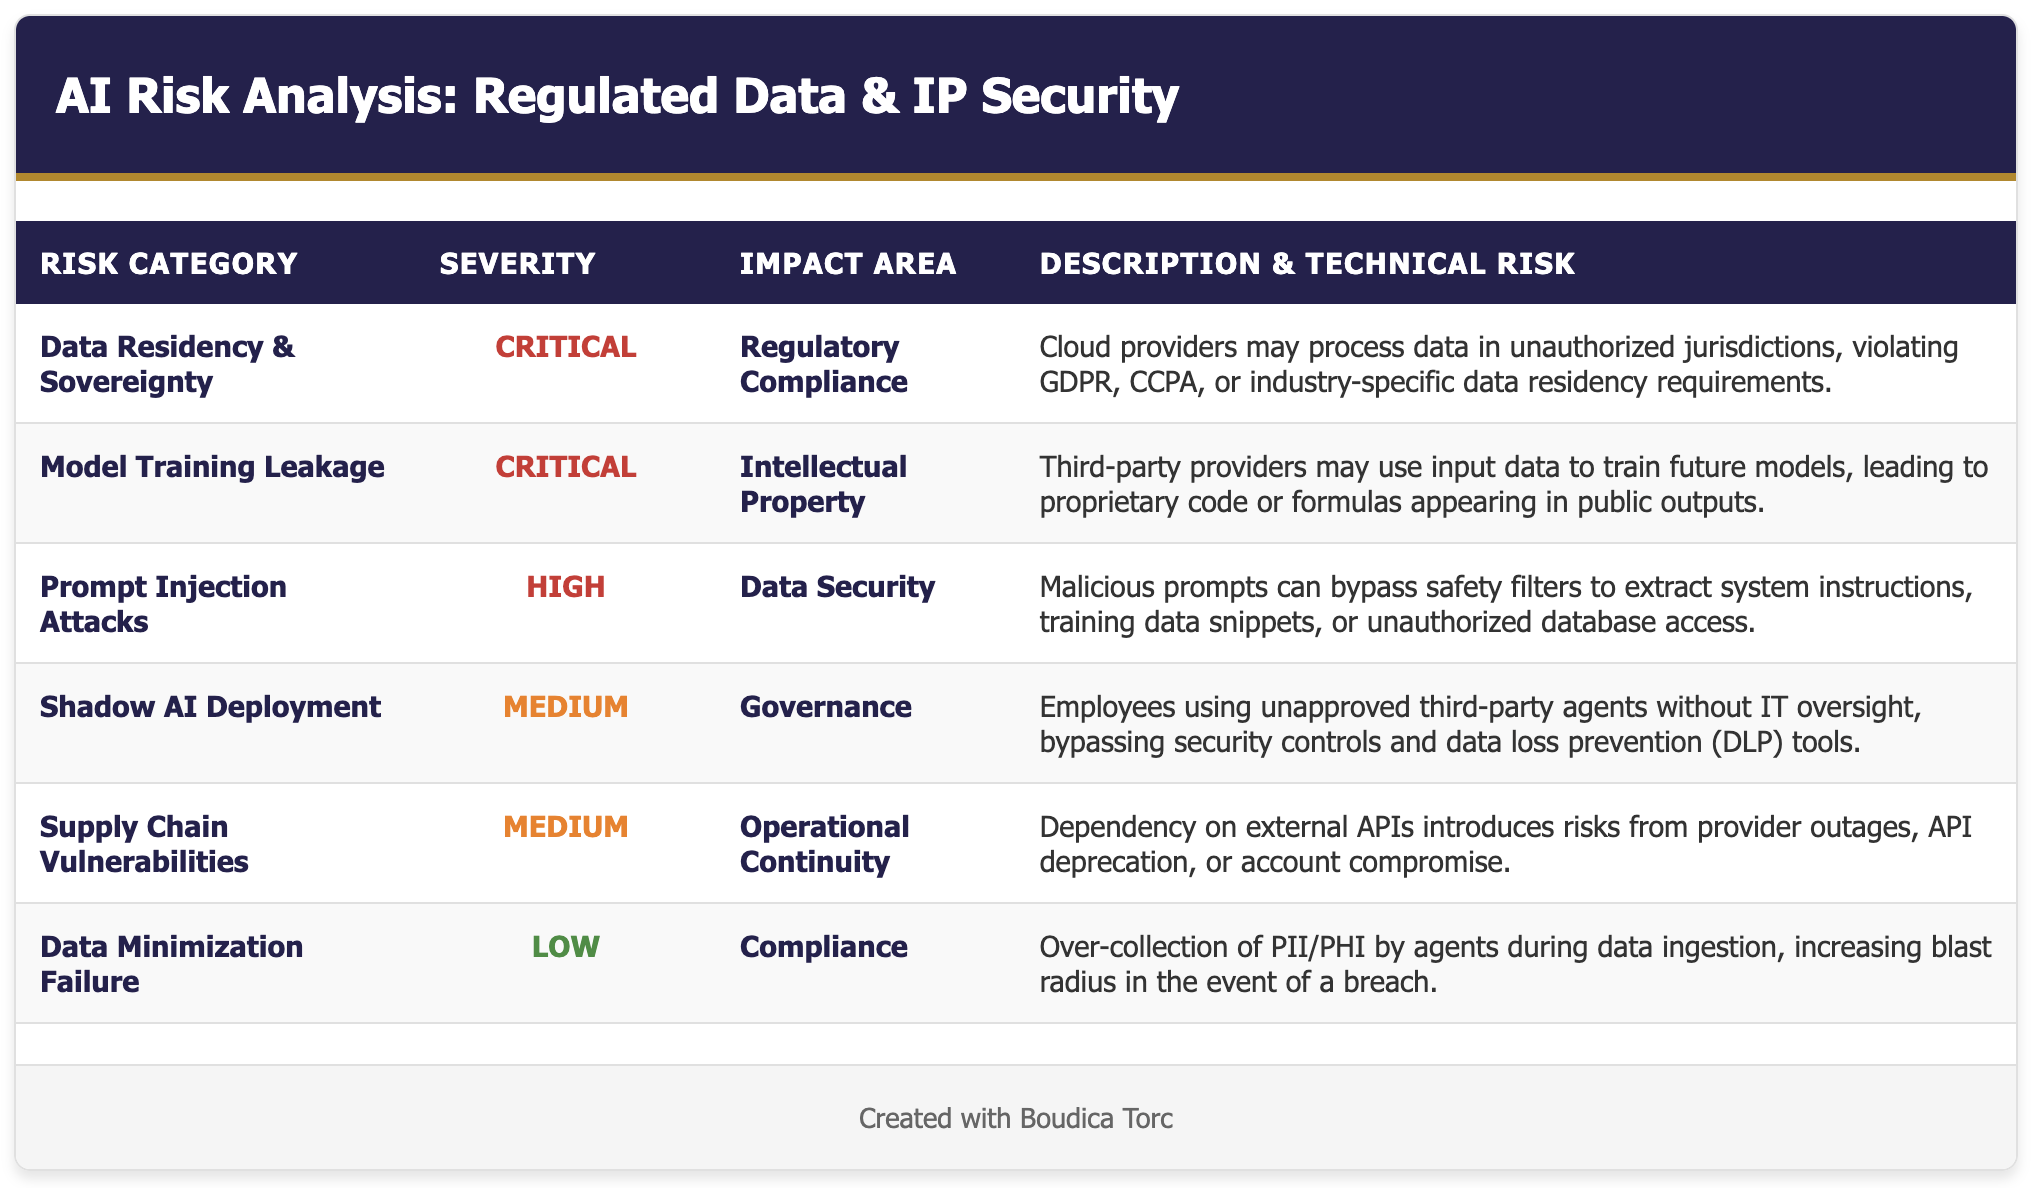
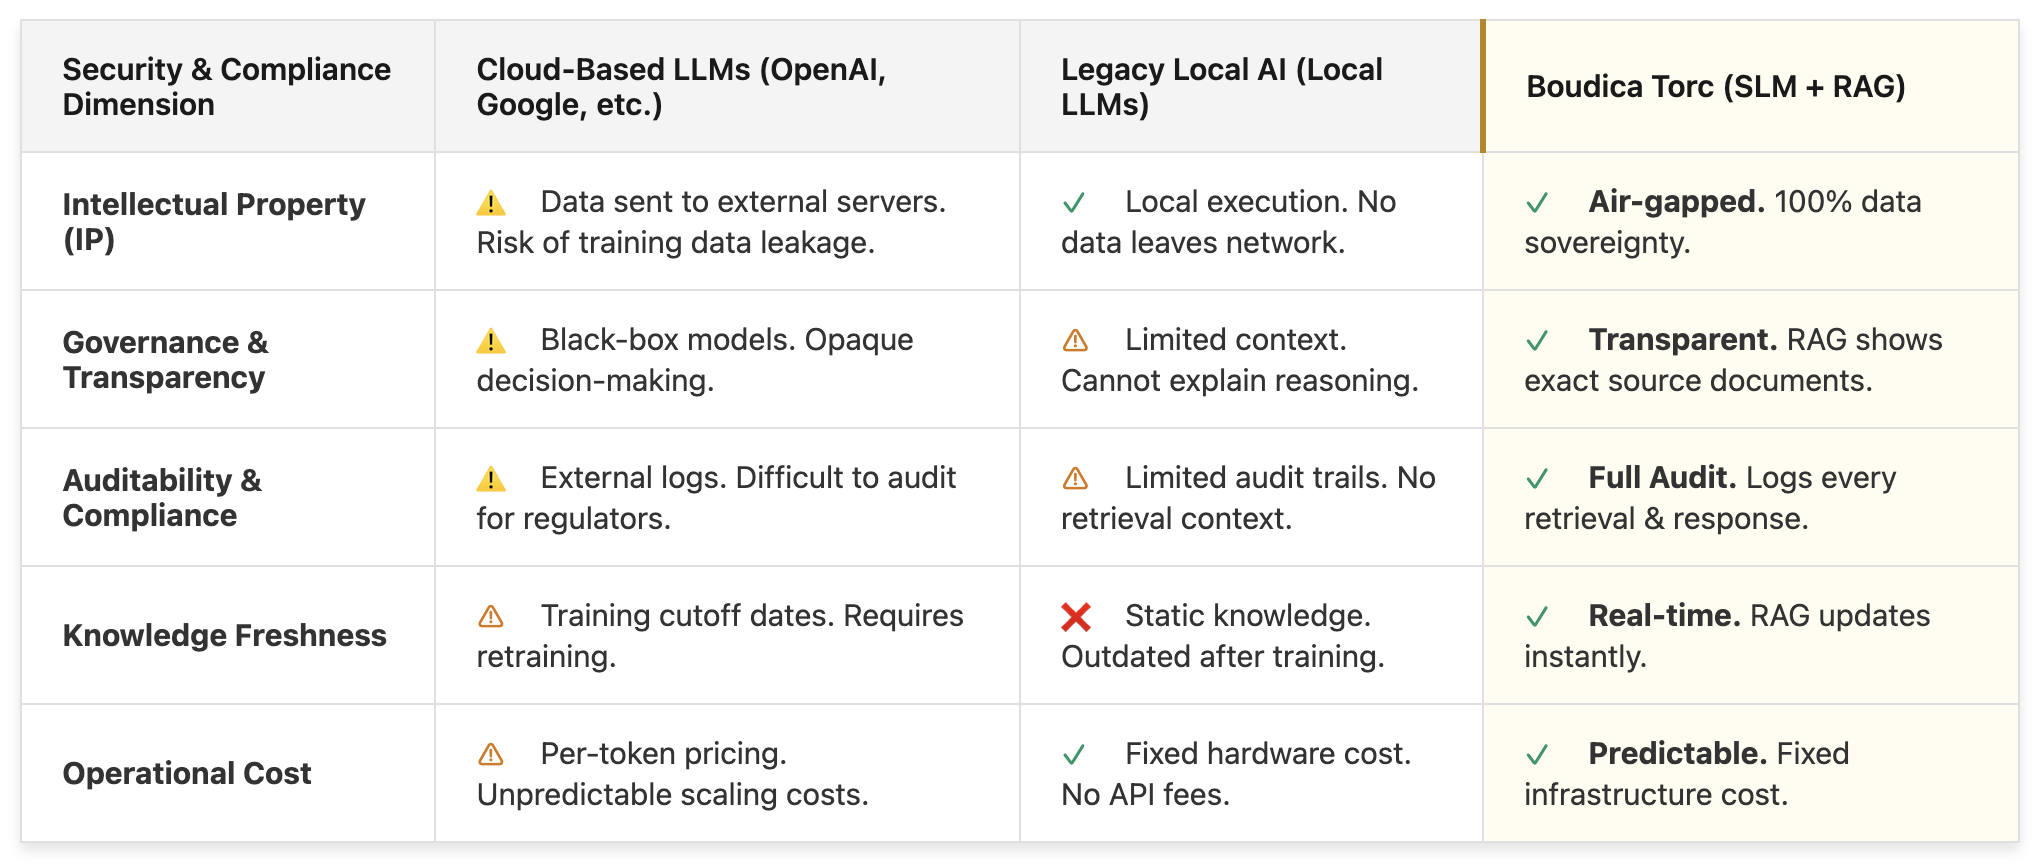
Every time you prompt a cloud-based LLM, you are sending your Intellectual Property & ideas out of your secure environment. This both risks your data, and means you cannot audit exactly how it has been used.
Never Risk Your IP.
Execute enterprise AI entirely within your firewall. No third-party API routing, zero data exfiltration, and auditable reasoning built for strict regulatory standards.
Own Your Own Intelligence.
Ironclad Perimeter Boundary
Total Air-Gapped Capability
Operate on your own hardware without an active internet connection for high-security environments, research labs, or edge deployments.
Regulatory Alignment Out of the Box
Purpose-built to satisfy strict requirements under the EU AI Act, HIPAA, GDPR, and defense-level compliance mandates by giving complete obervability of your data at all times with no third-party access or exposure.
Zero Third-Party Model Exposure
Prompts and document vectors are never transmitted across borders or used to train public foundation models.
01 / Deny-by-Default Access & Corpus Governance
Granular Document Security Built at the Database Level
Role & Departmental Access Control
Documents are classified (Public, Internal, Confidential, Restricted) and restricted by user role, department, or individual grant.
Pre-Retrieval Filtering
The RAG pipeline evaluates user permissions before searching the vector database, ensuring unauthorized text is never cited.
RAG Corpus Auditing
System administrators maintain full visibility to inspect, manage, or delete individual indexed text chunks across the organization instantly
02 / Sandboxed Extensibility & Operational Control
Safely Connect Enterprise Data Without Creating Security Holes
Containerized Connector Plugins
Custom ingestion scripts execute inside isolated, disposable containers with zero access to internal network assets.
Controlled Allowlist Web Crawling
Ingest external documentation using strict URL allowlists, completely blocking unguided or unsafe web scraping.
Human-in-the-Loop "Kill Switch"
Because inference runs on your infrastructure, halting AI execution is as immediate as stopping the local process or turning off the host server.
Key AI Sovereignty Use Cases
Healthcare & Life Sciences
Risk: HIPAA violations and loss of patient confidentiality. Research IP leakage to competitors.
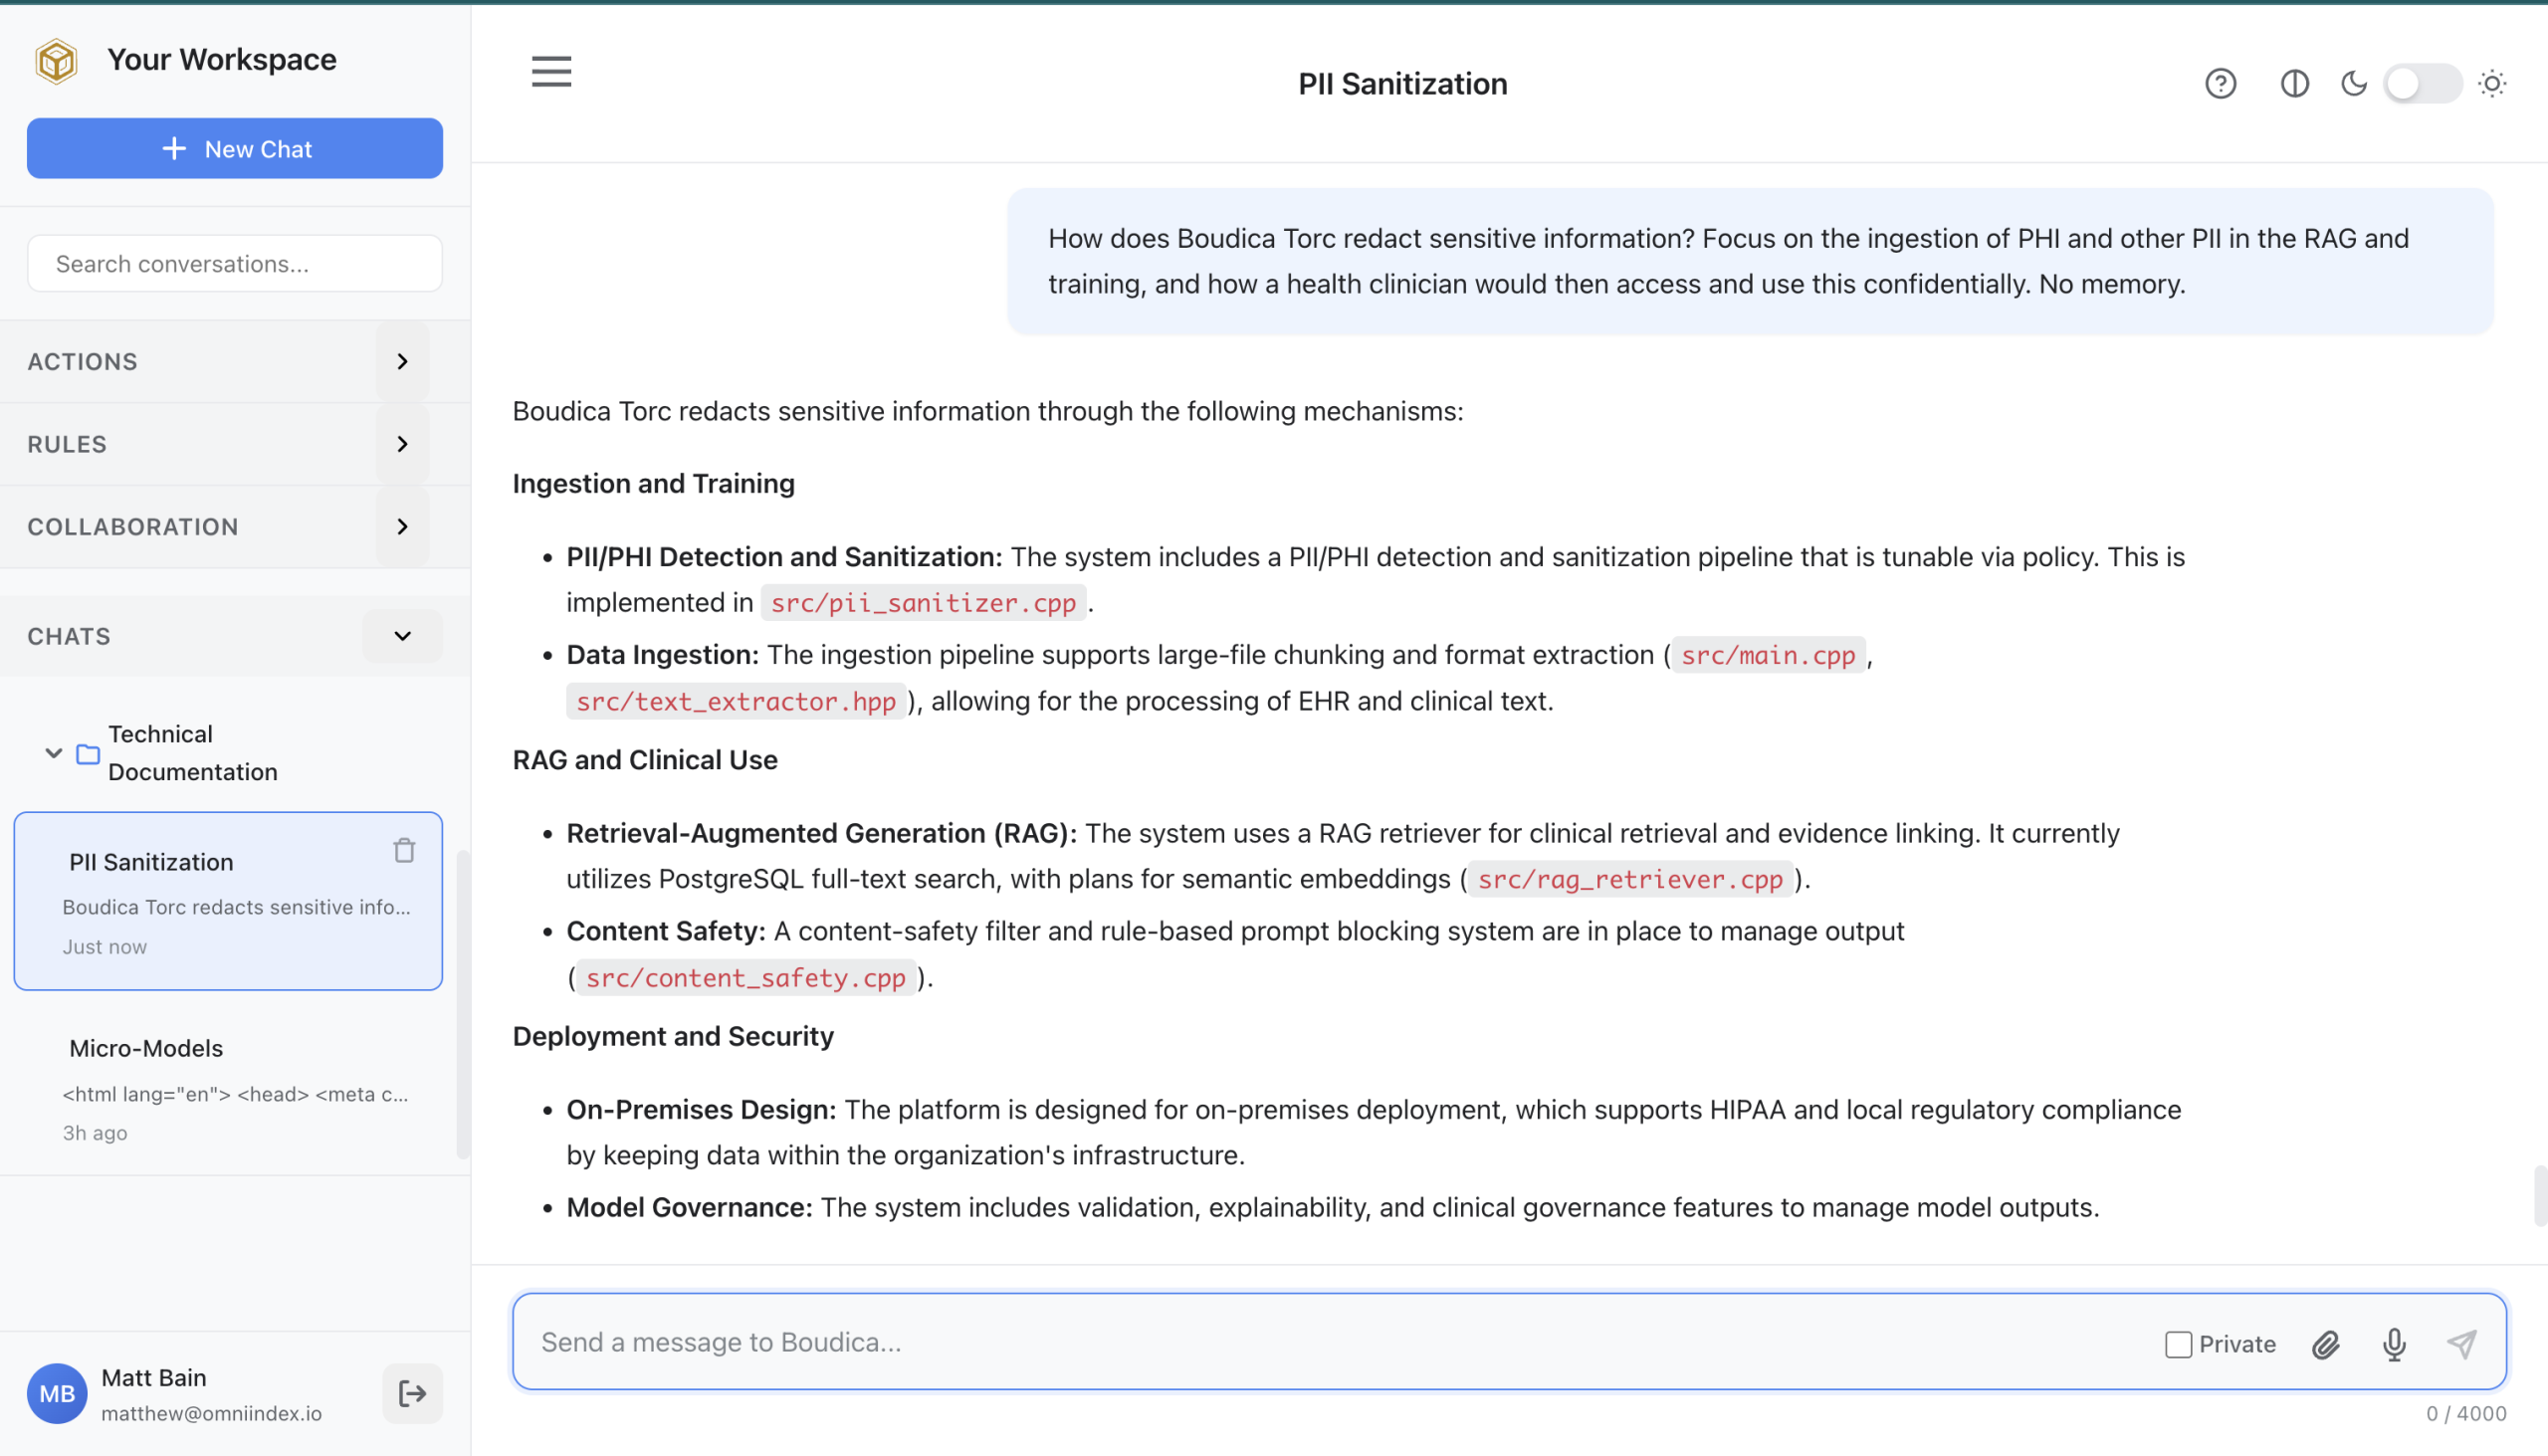
Boudica Solution: HIPAA-compliant architecture. RAG allows clinicians to query patient records without exposing data to the internet.
Financial Services & Banking
Risk: Regulatory non-compliance (GDPR, Basel III) if customer data is processed by third-party providers.
Boudica Solution: Complete data isolation. All PII remains within the bank's secure perimeter. Full audit trails for regulatory inquiries.
Defense & National Security
Risk: State-sponsored attacks on cloud APIs. Data exfiltration via API calls.
Boudica Solution: Air-gapped deployment. No internet connectivity required. Complete control over model weights and training data.
All rights reserved © 2026 OmniIndex